Hello
thanks for your answer
I did the following steps in order:
1- First, in the path you mentioned, I deleted the certificate that Openfire creates by default.
2- I entered the keys like this
For the certificate, I got a certificate from the letsencrypt site (free of course)
First, I went to /etc/letsencrypt/live/MY_DOMAIN.COM
Here there were files called cert.pem, chain.pem, fullchain.pem and privkey.pem.
I entered the content of the privkey.pem file in the Content of Private Key file: section
And then I entered the content of the fullchain.pem file in the Content of Certificate file: section
3- Then I saved and restarted the openfire service
But such a message is shown on the page.
please guide me.
Besides, on the site that I searched, some users were doing this by using keytool commands. Like the links below
https://discourse.igniterealtime.org/t/how-to-sucessfully-import-an-existing-startssl-cert-key-linux/57156
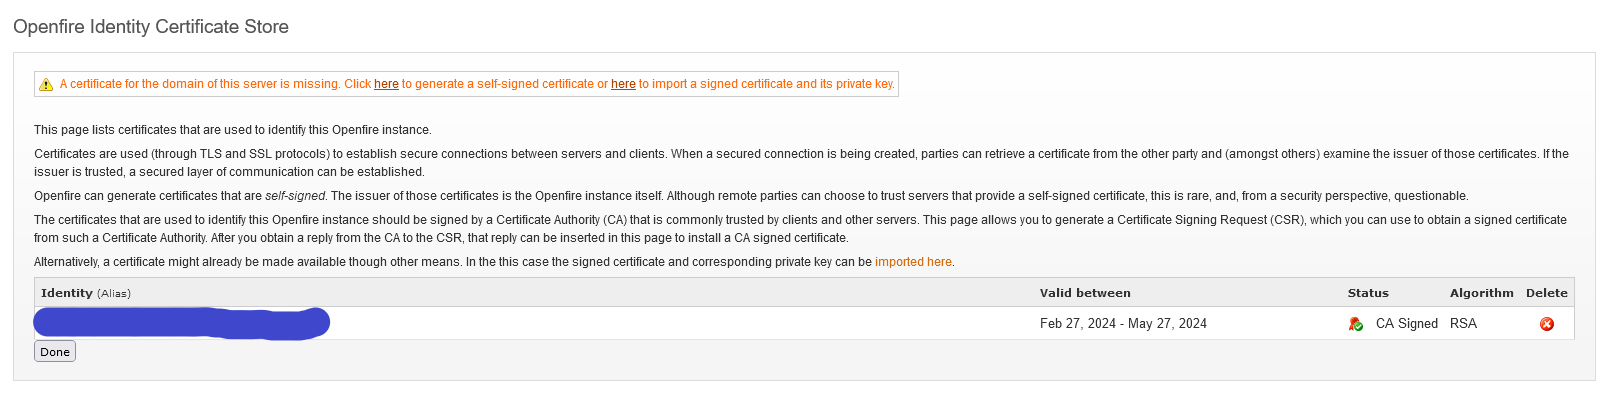
Please advise if there is anything